
VPC & subnets
VMware VLANs to VPC and subnets, three Swiss DCs, no SDN fabric to repurchase.
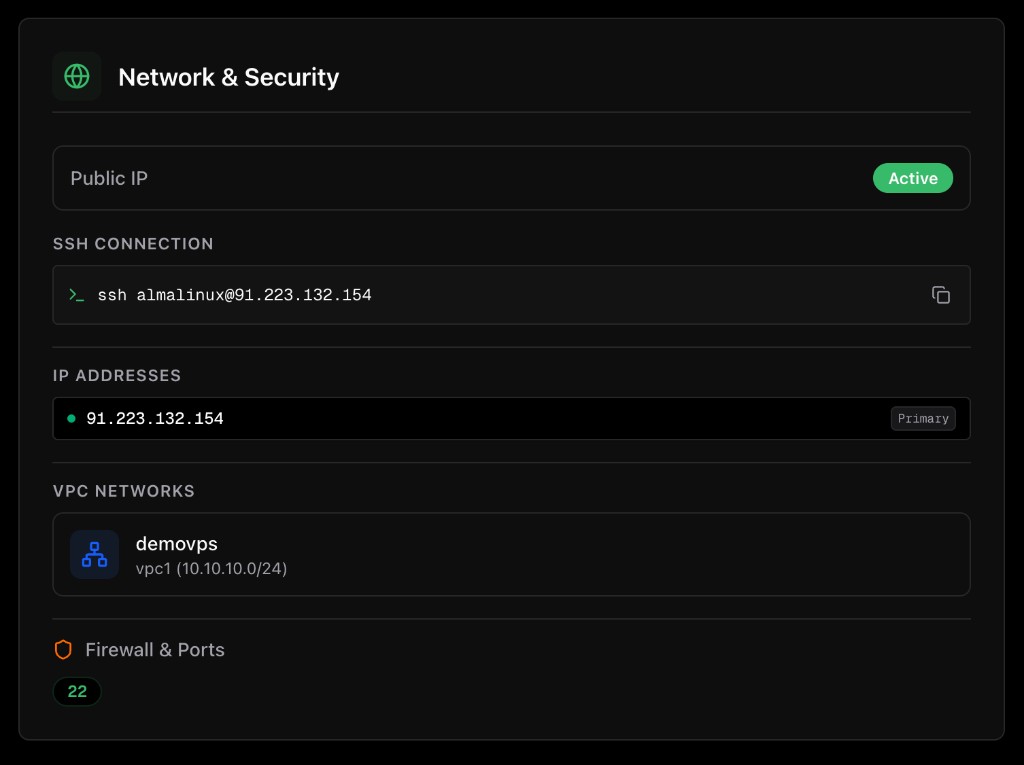
A Hikube VPC is a private network in your tenant, on Geneva, Gland and Lucerne. Subnets segment applications, data and administration. That is the VLAN / port-group mapping of a VMware exit: prod, DMZ, backup, admin. Isolation per project (network, storage, identities).
- VLAN to subnets
- Project isolation
- 3 interconnected DCs
- ISO 27001
- 3 DC
- SLA 99.99%
Typical VMware-exit case: map VLANs and port-groups to subnets. No proprietary fabric to relearn. Heavy NSX micro-segmentation needs a workshop: not everything maps 1:1. BGP is not a published SKU. VPN or site-to-site: talk to an engineer. Path: the VMware exit.
Capabilities
VLAN to subnets
Prod, DMZ, backup, GPU, admin. Anchor: how subnets are cut.
Project isolation
Network, storage, identities separated.
3 interconnected DCs
Private interconnect between Geneva, Gland and Lucerne. Public IPv4: 4 CHF/IP/month, failover across the 3 sites.
IN/OUT traffic
Not billed. Managed Kubernetes Ingress: 32 CHF/month.
No NSX to repurchase
VPC + subnets + API. Heavy NSX micro-segmentation needs a workshop.
API control
Hikube API and console. Terraform integration in preparation. Site-to-site VPN: an engineer.
In detail
Reuse VLAN logic: an app subnet, a data subnet, an admin subnet, optionally DMZ and backup. GPUs and databases do not need to share a broadcast with the bastion. The API declares subnets. A network workshop frames the addressing plan for a VMware exit. Hikube spreads Kubernetes workers automatically: you do not place nodes DC by DC.
No NSX to repurchase. The model is VPC + subnets + API. You do not learn a proprietary fabric to glue three VLANs. Highly specific NSX cases (complex micro-segmentation) need a workshop: not everything maps 1:1. On the way out: no fabric to buy back.
VPN or site-to-site: talk to an engineer. BGP is not a published SKU. Customer peering, if they already run it in their DC, stays a workshop topic, no published tariff line.
Without a VPC, every machine you create is an island with a public address, and the only barrier between your database and the internet is a firewall somebody has to remember to configure. A VPC inverts the default: nothing is reachable from outside until you decide it is. Concretely, it does four things.
- It keeps private what should be: a managed database listens inside the VPC and does not answer from the internet, with no configuration from you
- It separates what should not talk, by subnet: production, staging, backup, administration
- It connects your machines to each other without going through the internet: an application talks to its database on a private address, and that traffic does not leave
- It gives a single entry point from your premises, over VPN or a site-to-site link, instead of one public address per machine
- Per-tenant quotas and limits are not published here: if your addressing plan is constrained, have them confirmed before freezing it
Hidora SA operates the underlay, the three-DC interconnect, the VPC and FR/EN support. You keep the addressing plan, application ACLs, the bastion and public exposes you justify. Terraform integration in preparation: today, Hikube API and console.
VMware exit: remap prod, DMZ, backup, admin. Databases and brokers off the internet. Isolated GPUs. Kubernetes in the same tenant. Healthcare and finance: per-project isolation for the DPIA. Instances page: cloud instances.
Public IPv4: 4 CHF/IP/month, failover across the three sites. IN/OUT traffic not billed. Managed Kubernetes Ingress: 32 CHF/month. BGP is not a published SKU. VPN or site-to-site: engineer framing, no published line. Pricing page: the pricing page.

Frequently asked questions
No. Hikube is a sovereign cloud: compute, storage, backups and metadata stay on three independent Swiss datacenters (Geneva, Gland, Lucerne). There is no replication to the EU or the United States.
The operator is Hidora SA, a Swiss company in Lancy (Geneva), with no US parent. Compute, storage, backups and metadata stay in Geneva, Gland and Lucerne. That is not the same legal basis as AWS, Azure or GCP. We are not your counsel: GDPR for EU data in Switzerland relies in particular on adequacy.
Through the Hikube API and the console. Terraform and Cluster API integration in preparation. kubectl, Helm and S3 clients stay. Docs: docs.hikube.cloud.
Yes: how subnets are cut describes the split. There is no separate V1 page.
No. Hikube automatically distributes workers across Geneva, Gland and Lucerne. Pod topology spread stays yours.
No. IN/OUT traffic is not billed, as published. Public IPv4: 4 CHF/IP/month. Kubernetes Ingress: 32 CHF/month.
Yes. Hikube is Swiss cloud IaaS (VMs, managed Kubernetes, GPU, S3, backup, vault) operated by Hidora SA on three datacenters: Geneva, Gland, Lucerne. Published SLA 99.99%, ISO 27001, engineer support in French and English. It is not shared web hosting. GPUs are in the 14-day trial. Windows Server is a licensed image on instances.
Ready to run on 100% Swiss infrastructure?
14-day trial, no credit card. GPUs included.